Aura
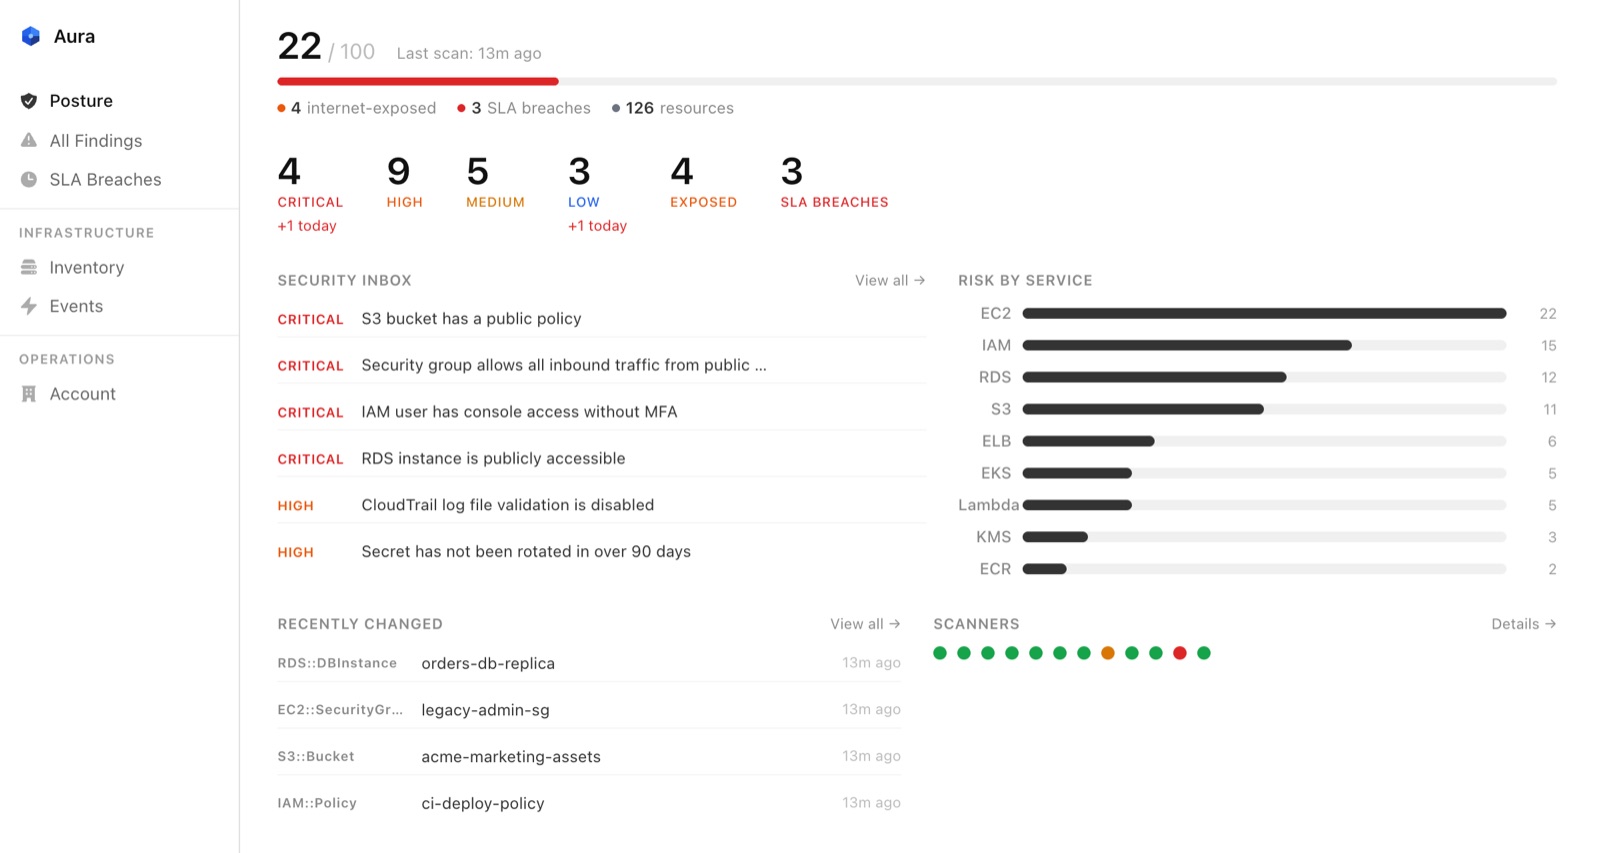
Aura shows a company what it's running on AWS, what's exposed and how to fix it. Built by our team. The screens show sample data.
- For
- Smaller companies running on AWS
- Stack
- Go, PostgreSQL, Starlark, React, AWS
- Built
- 2026, over 2 to 3 months
The problem
Cloud security platforms are excellent, and priced for enterprises. Many smaller companies can't justify them, so they run AWS without really knowing what they have or what's exposed. One leaked access key or one public bucket is enough to cause real damage.
What was built
-
See what you have
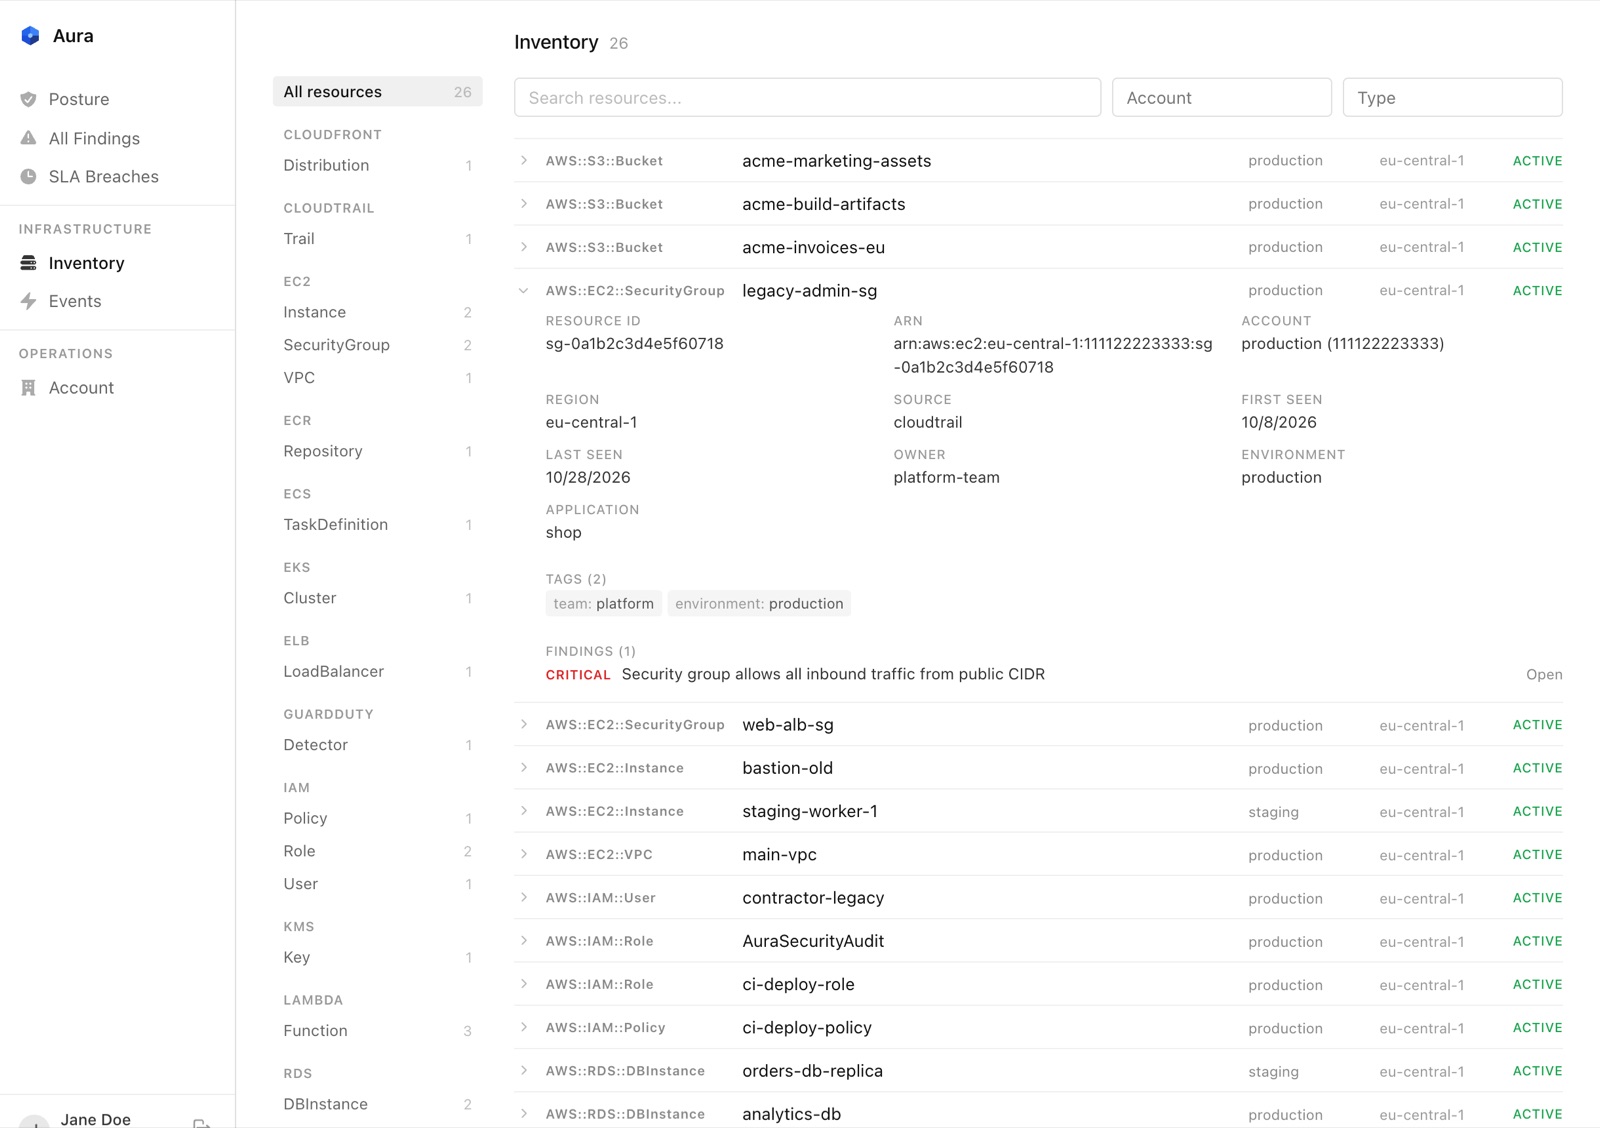
One up-to-date view of what's running in the account, so forgotten resources don't stay hidden.
-
Hear about risks right away
A risky change shows up within moments, not at the next scan.
-
Checks that keep up
New security checks go live without a new release, and automated tests catch mistakes first.
-
Know what to do next
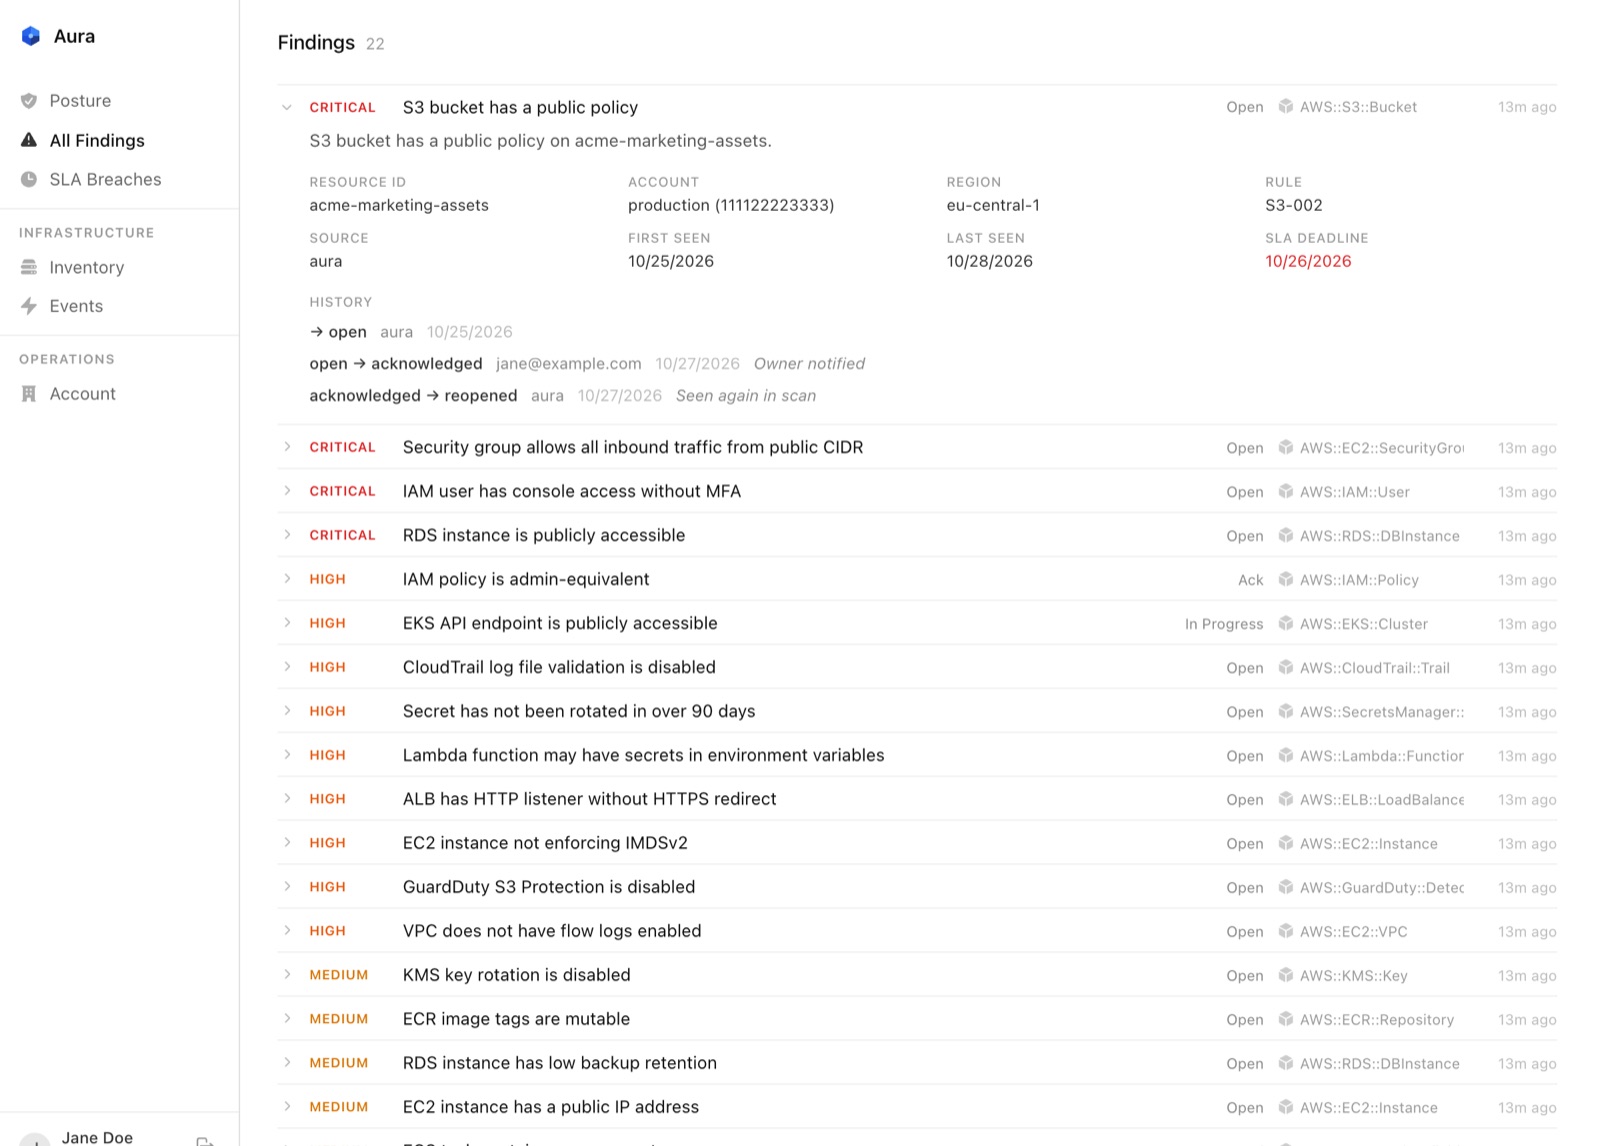
Each risk comes with the steps to fix it, a deadline to track and alerts, so it doesn't get forgotten.
Key decisions
Inventory first
An accurate picture of the account comes before any rule, so later layers can be added without a rewrite.
Don't rebuild AWS
Findings from GuardDuty, Security Hub, Inspector and IAM Access Analyzer sit next to Aura's own.
No noise
Findings resolve themselves when fixed and reopen if the problem returns.
What's next
Today each account is added by hand, so onboarding through AWS Organizations comes next. So does a network graph, to tell whether an open port can really be reached from the internet.
Read the full technical write-up